

Alliance Healthcare Group disclosed in a Singapore Exchange filing on 24 October 2026 that unauthorised access to its subsidiary Alliance Medinet’s membership database compromised the personal data of about 110,000 members, in a breach that cybersecurity commentators say shows why insurers must govern third-party administrators as tightly as their own systems.
Key Takeaways
- A breach at Alliance Medinet, a third-party claims administrator serving at least six insurers, exposed the personal data of about 110,000 members, including NRIC numbers and contact details.
- HSBC Life, Singlife and Income Insurance confirmed affected customers while saying their own systems stayed intact — the compromise sat entirely with the shared administrator.
- Keeper Security cites Verizon data showing third parties were involved in 48% of breaches, a 60% increase on the prior year, and says only 38% of APAC organisations have fully deployed privileged access management.
One Administrator, Six Insurers, One Breach
Alliance Medinet is a third-party administrator that processes claims and corporate health benefits for insurers. The exposed data includes names, personal identification numbers and contact details; seven members may have had bank account information exposed, and one member’s medical diagnosis may have been accessed. Alliance Medinet reported the incident to Singapore’s Personal Data Protection Commission (PDPC) on 21 October, engaged independent forensic specialists, and added 24-hour network and dark web monitoring.
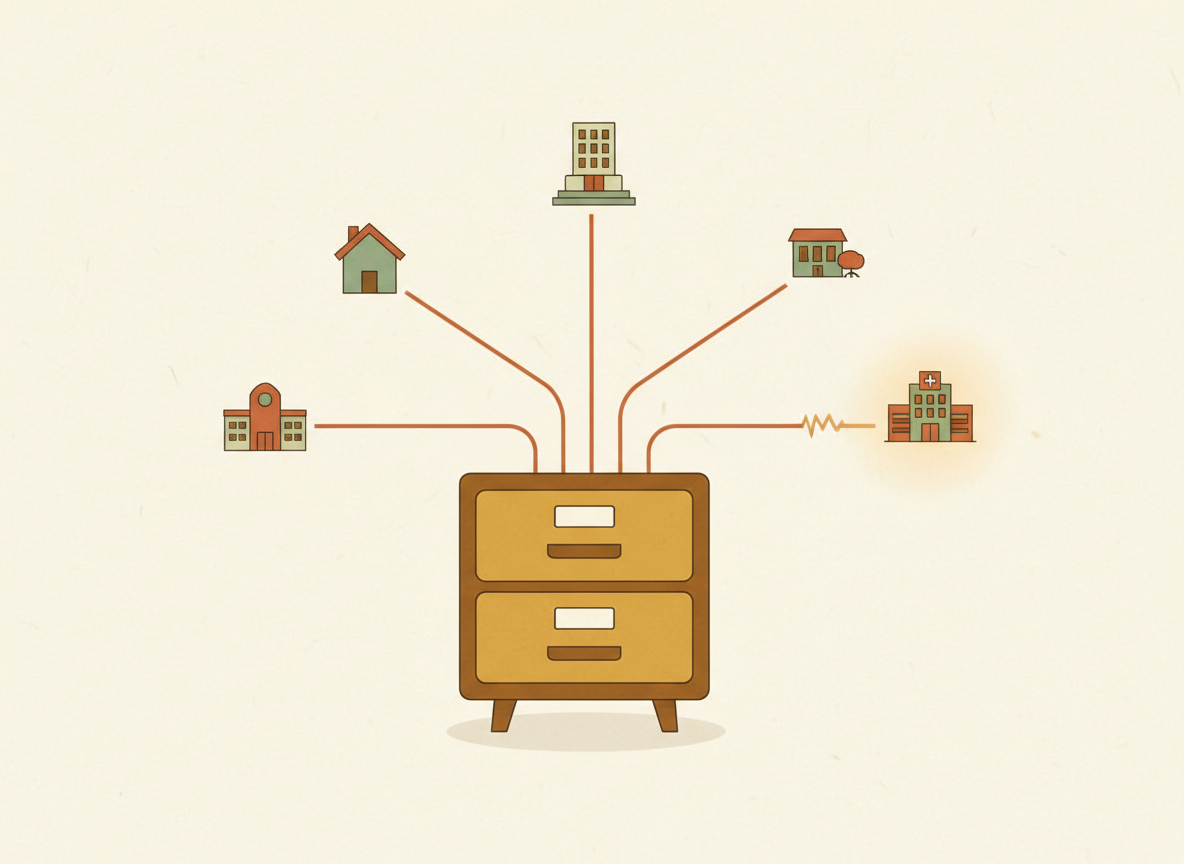
“Third-party administrators sit between insurers and their policyholders, holding identity and policy data from many principals in a single system. That concentration is efficient for claims processing, but it creates an exceptionally lucrative target for cybercriminals: one intrusion at the administrator reaches the customers of every insurer it serves,” said Takanori Nishiyama, Senior Vice President, APAC & Japan Country Manager at Keeper Security.
Why NRIC Exposure Is Different
Nishiyama noted that policyholders’ National Registration Identity Card (NRIC) numbers and dates of birth, unlike passwords, cannot simply be reset. Singapore’s PDPC heavily restricts NRIC collection for exactly this reason, yet healthcare and insurance providers must still process them — meaning administrative databases like Alliance Medinet’s remain some of the most sensitive assets in the sector, even though policyholders and regulators will draw no distinction between an insurer and the administrator it hands data to.
Closing the Privileged Access Gap
Keeper Security’s research found that while 59% of organisations in Asia-Pacific use single sign-on, only 38% have fully deployed privileged access management, leaving broad standing access to customer data long after a task ends. Nishiyama recommends a zero standing privilege model that grants just-in-time access, enforces least privilege on every human and non-human identity, records privileged sessions, and flags bulk queries or exports in real time — alongside actively auditing and removing dormant accounts the moment a client or contractor relationship ends.